5 Ways to Protect Your Cybersecurity Posture
When you look back 30 years ago, IT’s job was drastically different. Antivirus was available on numerous floppy discs, people were writing their passwords on sticky notes or pads...
Meet evolving regulatory demands with smart, scalable controls that support your most critical operations. From designing access controls to policy implementation and real-time reporting, we help you stay aligned with CMMC, NIST, CIS Critical Security Controls, and ISO.

We help you identify and align with the right compliance standards so you're built for success from the start.

We write and refine practical, audit-aligned policies that map directly to your regulatory requirements and business operations.

Our experts evaluate your current state, uncover compliance shortfalls, and deliver a clear, prioritized roadmap to get you where you need to be.

We support you through the full audit lifecycle—preparation, documentation, auditor coordination, and post-audit action plans.

We implement technical and administrative controls that meet your compliance needs without disrupting your workflows.

We help you achieve and maintain compliance. Our team continuously monitors control health, flags drift, and ensures configurations remain aligned with evolving frameworks, so you're always audit-ready.

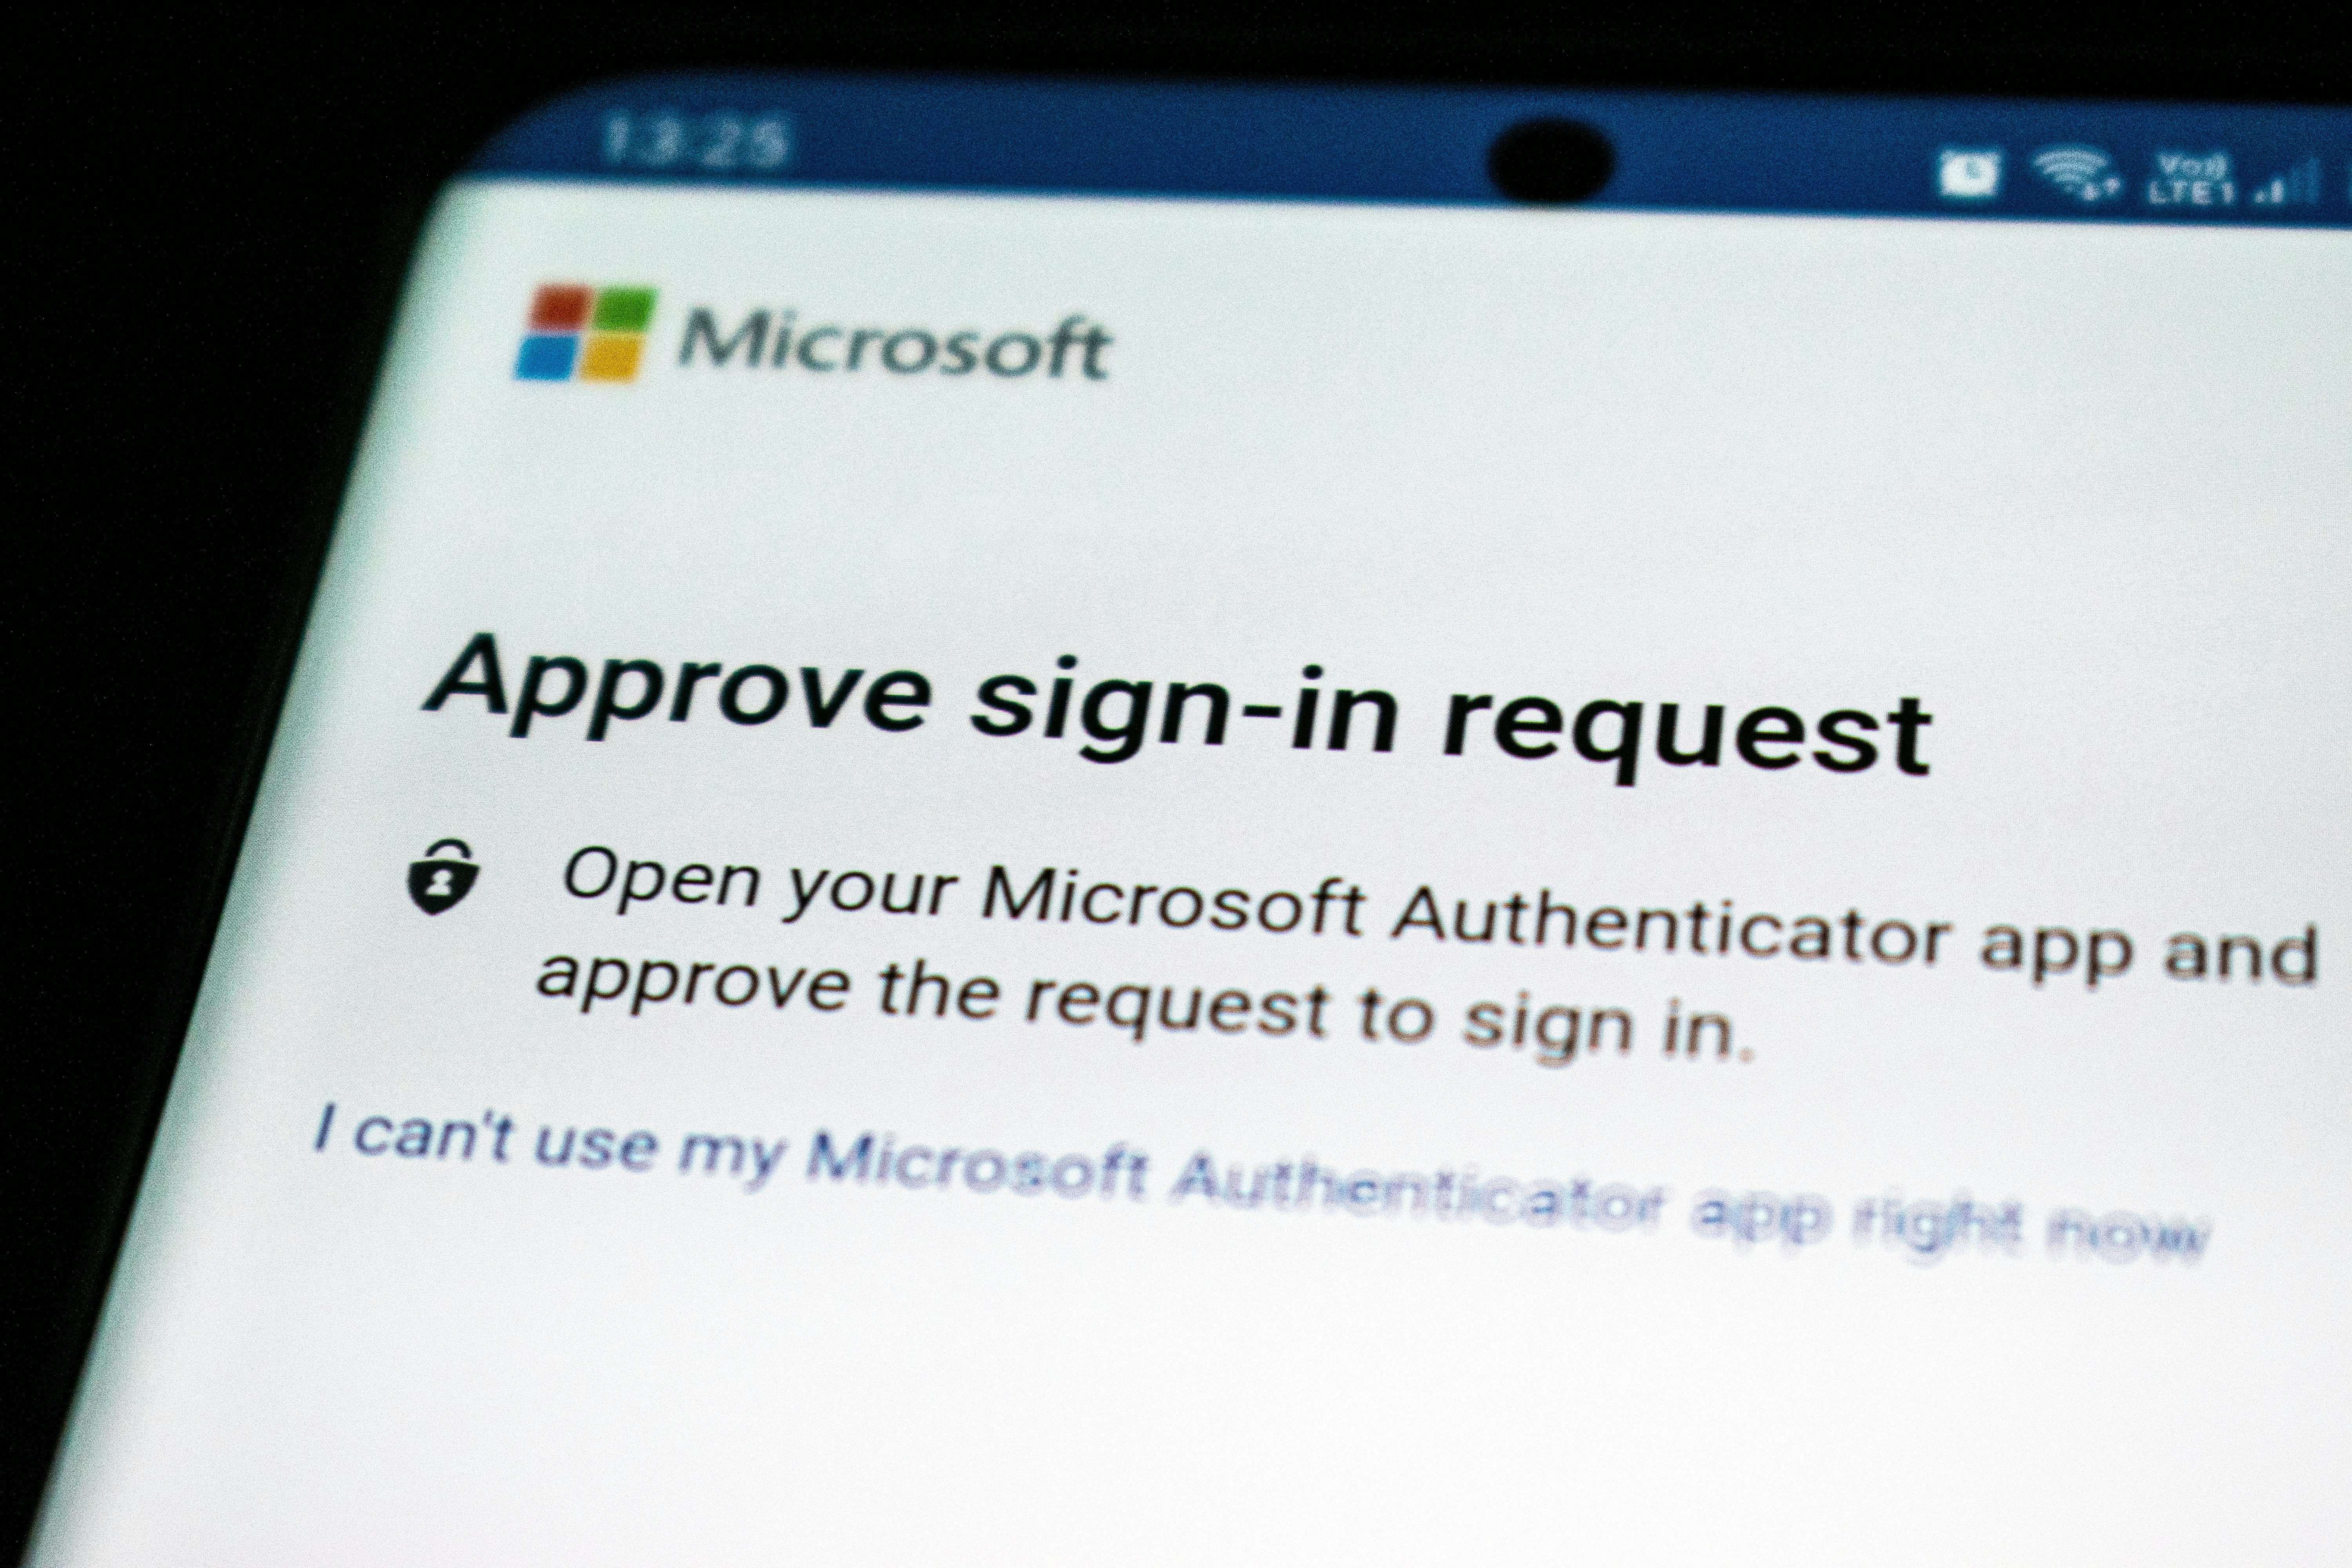
When you look back 30 years ago, IT’s job was drastically different. Antivirus was available on numerous floppy discs, people were writing their passwords on sticky notes or pads...
What would your team do if a request for customer records arrived from a real government email address?
If the answer is "fulfill it," you now have something in common with...
Credit unions occupy an awkward spot in the threat landscape. You hold the same sensitive member data and move the same money as a big bank, but you do it with a fraction of the...
Credit unions face a security landscape that grows more demanding every year. Between evolving NCUA expectations, the FFIEC cybersecurity assessment tool, and rising ransomware...
Here’s a statistic from our recent webinar that may come as a surprise: roughly 90% of security failures happen on the phone.
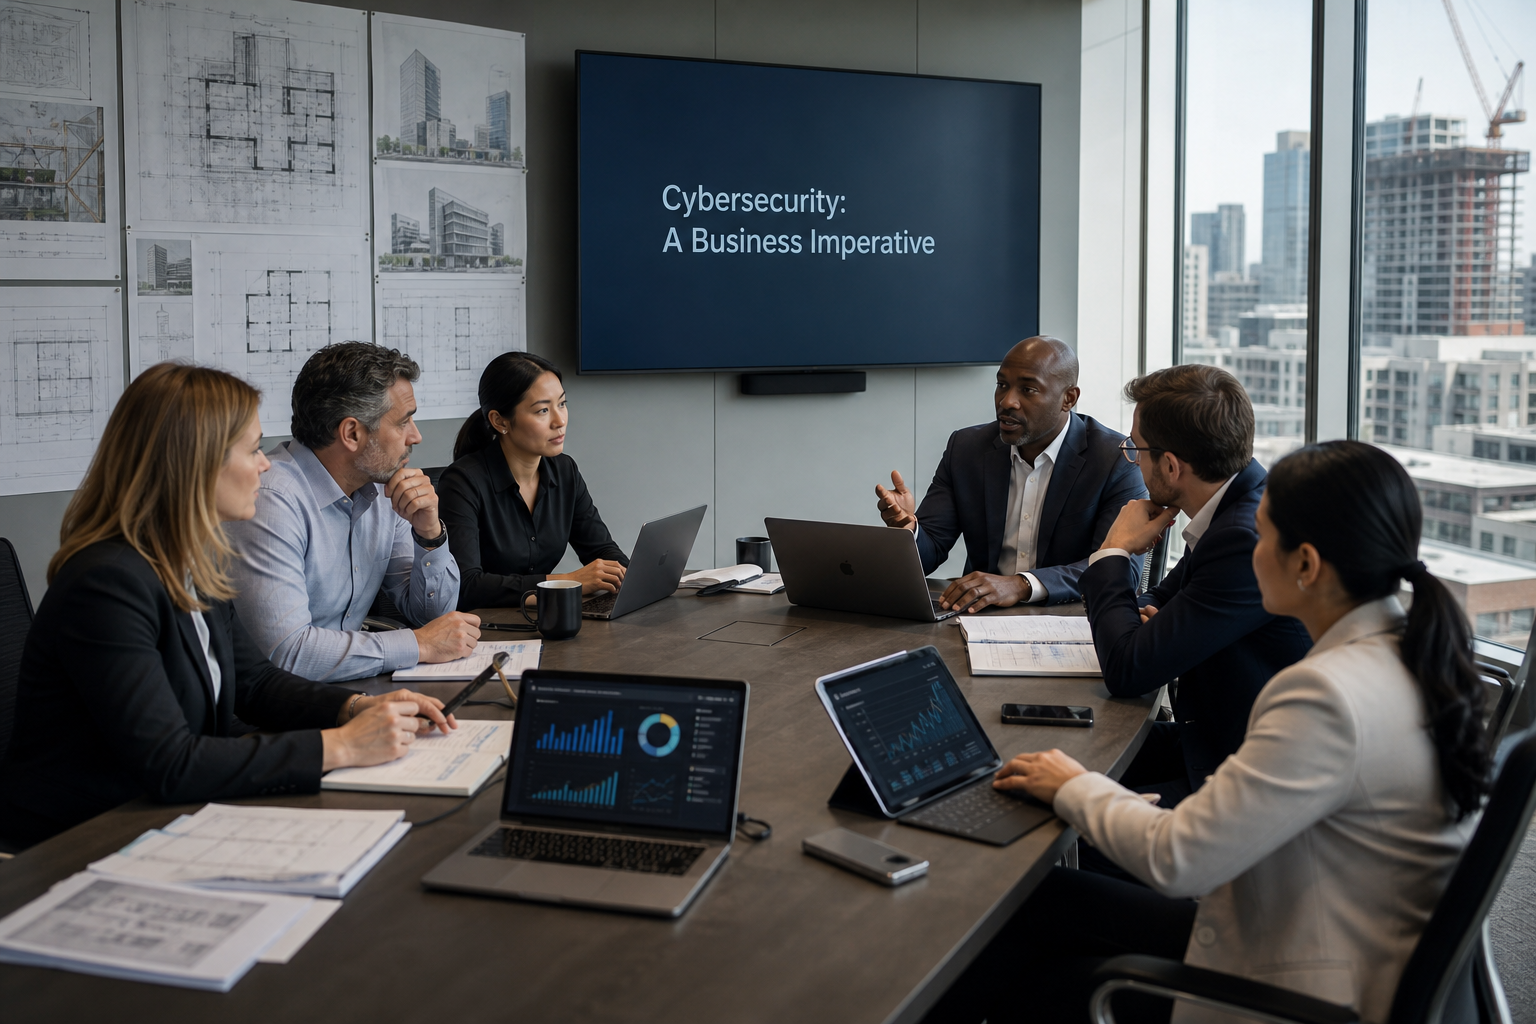
If you lead an architecture, engineering, or construction firm and you still think of a cyber attack as something that happens to other companies, this blog...
When a ransomware attack hits, leaving your online banking down and your phones ringing off the hook, your first instinct may be not to say what is going on.
But your team...
Your core system goes down at 10:02 a.m. Members can’t access accounts. Branch staff are staring at frozen screens. Your IT lead is knee-deep in logs.
Quick. Who:
Calls the...

On June 12, 2026, the U.S. government issued an export control directive that forced Anthropic to disable Claude Fable 5 globally, less than 72 hours after its public release....

It’s easy to believe that preventing a cybersecurity disaster hinges on having the latest tools, the most advanced AI, or the biggest budget. If you walk any conference floor or...